
Two critical flaws in PHP, nicknamed PHP2Shell, made headlines this week. If your website is hosted with The BBS Agency or one of our preferred hosting partners, attack traffic was being blocked before the official fix shipped, and we are now finishing the server updates.
Here is what happened, how your site was protected, and what (if anything) you need to do.
What is PHP2Shell?
PHP2Shell is the name for two critical vulnerabilities in PHP, tracked as CVE-2026-109618 and CVE-2026-109619. The PHP security team rated both 9.2 out of 10 for severity (Tenable).
PHP is the software running on the web server that builds your pages. It powers a large share of the internet, including every WordPress site. Because these flaws are in PHP itself, any site on an unpatched PHP version is exposed, no matter how the site was built (Patchstack).
In the worst case, an attacker could run their own code on a vulnerable server without logging in. That is why this got so much attention.
In the worst case, an attacker could run their own code on a vulnerable server without logging in. That is why this got so much attention.
The timeline moved fast:
| Date (UTC) | What happened |
|---|---|
| Oct 21, 14:00 | PHP released fixed versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35 |
| Oct 21, 03:02 | Cloudflare’s firewall rules went live for all customers |
| Oct 20 | Details leaked ahead of the planned disclosure |
| Oct 17 | Earliest reported exploitation attempts (Amazon Threat Intelligence) |
Sources: Sansec, Cloudflare, Tenable.
How Cloudflare blocked attacks before the patch
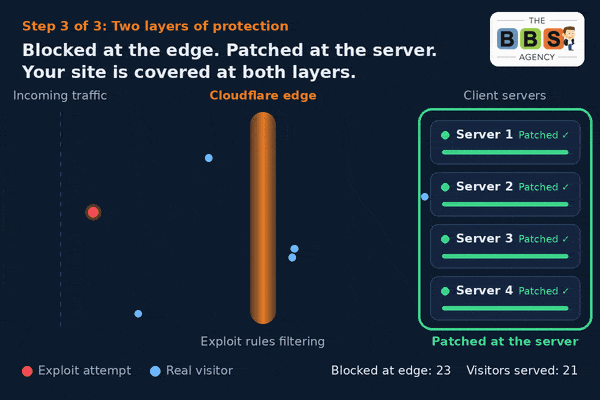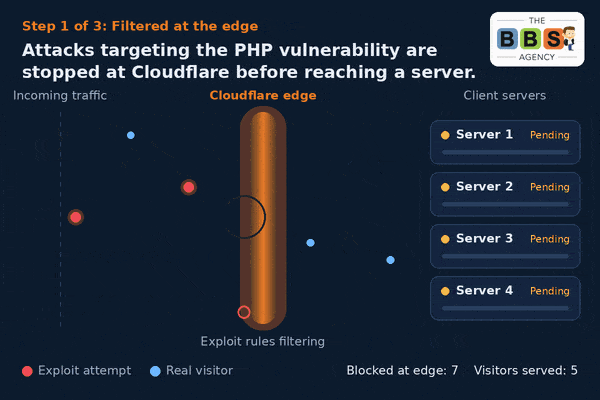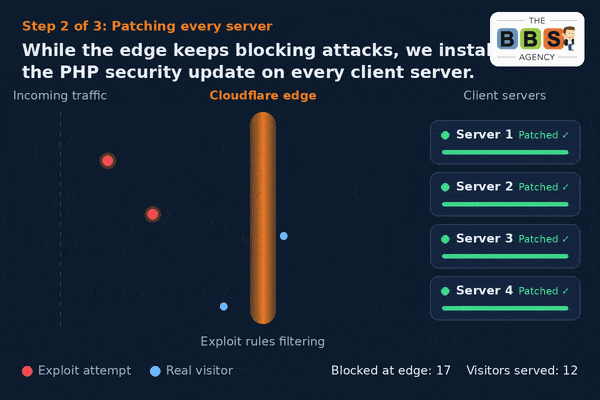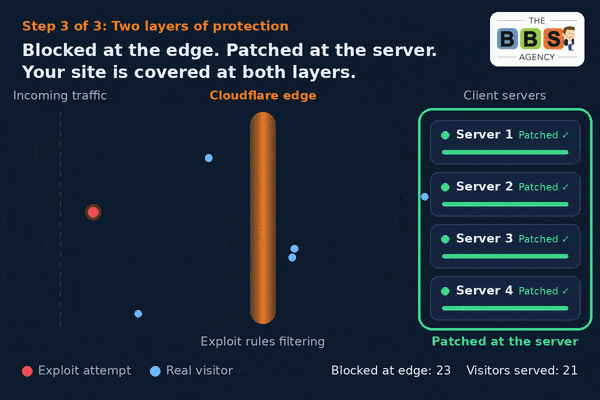
Our hosting partners route website traffic through Cloudflare, which sits between your server and the rest of the internet. Every request passes through Cloudflare’s firewall before it reaches your site.
Cloudflare was part of the coordinated industry response to PHP2Shell, working with the PHP Foundation, OpenAI and Wiz. Its firewall rules for these flaws were protecting customers by default from 3:02 a.m. UTC on October 21, about 11 hours before PHP released its fix (Cloudflare).
That meant exploit attempts were stopped at the edge, before they ever touched a client server. Cloudflare itself calls these rules a stopgap, not a replacement for patching (Tenable). They bought our data center teams the time to roll out the real fix safely.
Patching every server
Our hosting teams are installing the official PHP security updates across every client server. Most servers are already patched, and we expect the rest to be finished by the end of the day on October 22. We will update this post when every server is confirmed.
Once patching is complete, your site is protected at two layers: attacks are blocked at Cloudflare, and the vulnerability is fixed on the server itself.
What you need to do
If we host your site, nothing. Your website should keep running normally while we finish the updates.
If your site is hosted somewhere else, ask your host two questions today:
Has the server been updated to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 (or newer)?
If you use a firewall like Cloudflare, does the server only accept traffic that comes through it? Firewall rules only help if attackers can’t reach the server directly (Patchstack).
If you don’t get clear answers, we’re happy to take a look.
FAQ
Does PHP2Shell affect WordPress sites? Yes. WordPress runs on PHP, so any WordPress site on an unpatched PHP version is exposed. Updating WordPress or its plugins does not fix it; the PHP version on the server has to be updated.
Was my site hacked? We have no indication that any site hosted with BBS or on a Care Plan was compromised. If we find otherwise, we will contact you directly.
Do I need to change my passwords? Not because of this issue. Good password hygiene is always worth it, though.
Is Cloudflare protection enough on its own? No. Cloudflare’s rules are a stopgap that block known attack patterns. Patching PHP on the server is the real fix, which is why we’re doing both.
Why we host the way we do
This is exactly why we offer hosting and care plans and only work with providers we trust. When a vulnerability like this hits, our job is to handle it so you can keep running your business.
Questions about your site, or want us to check a site hosted elsewhere? Contact The BBS Agency.